TECHFUND
Media
WOOFi $8.5 Million Exploit | Hack Analysis
WOOFi Hit by $8.5 Million Flash Loan Attack on Arbitrum (March 5th)
Summary
On March 5th, WOOFi, a well-known decentralized exchange (DEX) operating across different blockchains, fell victim to a flash loan attack on the Arbitrum network, resulting in a substantial loss of around $8.5 million.
Understanding the Attack
The Exploit: The attacker targeted WOOFi's swap contract, artificially inflating the price of the WOO token through strategic swaps. This manipulation led to a significant drop in the token's value.
Root Cause
The attacker used flash loans to borrow both USDC and WOO tokens. Then, they cleverly manipulated swaps within WOOFi to make the WOO token price shoot up. After that, they dumped a large amount of WOO tokens to crash the price even lower. By doing this, they could buy back WOO tokens at a reduced price. With these tokens, they repaid the loans they borrowed and converted the stolen WOO tokens into cash
- The attacker commenced the attack by acquiring funds through a flash loan.
- They obtained a total of 10,504,796 USDC and 2,721,172 WOO.
- Collateralizing 7,000,000 USDC, they borrowed 5,092,663 WOO from Slio Finance.
Price Manipulation of the WOO Token
- The attacker used $300,000 USDC in WOOFi.
- They traded multiple times, boosting the WOO token price from 56,884,100 to 60,400,479.
- The critical moment came when they exchanged 8,196,117 WOO for USDC.
- This caused a massive drop in the WOO token price to 0.00000007.
- The decrease was staggering, at 8.62 million times lower than before.
The attack exploited a flaw in WOOFi's pricing mechanism, which relied solely on oracle data and overlooked the possibility of manipulation.
Contract code revealed a flaw in the price data processing mechanism during the conversion of BaseToken to QuoteToken, _calcBaseAmountSellQuote function.
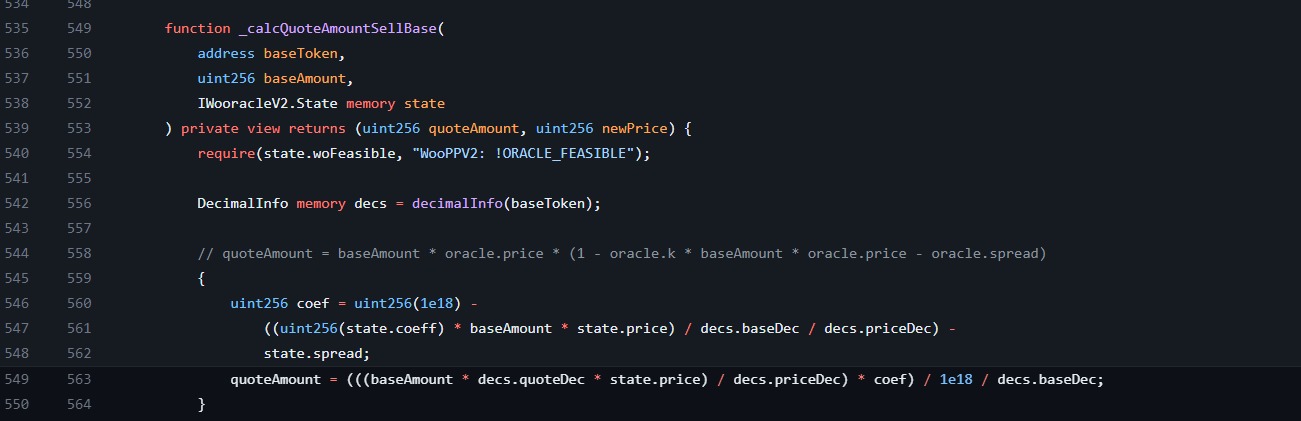
The main vulnerability is direct calculating the amount by multiplying and dividing based on the price, so that there is no slippage in the exchange process but the price will change with the rate
 // newPrice = oracle.price * (1 - 2 * k * oracle.price * baseAmount)

newPrice =  ((uint256(1e18) - (uint256(2) * state.coeff * state.price * baseAmount) / decs.priceDec / decs.baseDec)*state.price) / 1e18;
    }
Mitigation of this vulnerability ?
The adjustment factor (uint256(1e18) - (state.coeff * state.price * baseAmount) / decs.priceDec / decs.baseDec) ensures that the new price calculation considers the impact of slippage and prevents potential price manipulation.
// newPrice = oracle.price  (1 - k  oracle.price * baseAmount)

newPrice = ((uint256(1e18) - (state.coeff  state.price  baseAmount) /        decs.priceDec / decs.baseDec) * state.price) / 1e18
Additional
- Affected WOOFi Swap Contract Address: 0xeff23b4be1091b53205e35f3afcd9c7182bf3062
- Transaction Hash of the Attack: 0xe80a16678b5008d5be1484ec6e9e77dc6307632030553405863ffb38c1f94266
Learn more about Flash loan Attack
Author : Piyush Shukla